Essential Points
- SHA-256 converts any data into a 256-bit fingerprint, written as 64 hexadecimal characters, and the same data always produces the same hash.
- Calculating a hash is immediate, but undoing it is not feasible with current computing, and changing a single character alters the entire result.
- Bitcoin applies double SHA-256 to the header of each block, and in August 2026 the network was calculating about 900 EH/s.
- SHA-256 is useful for verifying integrity and signatures, but not for storing passwords on its own: OWASP recommends Argon2id.
Each time a Bitcoin miner attempts to close a block, it repeats the same calculation: applying the SHA-256 algorithm twice to the block header and checking if the result meets the network's target. In August 2026, the entire network was processing approximately 900 exahashes per second (EH/s), or about 900 trillion hashes per second—a rate no home computer could match.
A hash is a digital fingerprint of a piece of data, and the SHA-256 hash always occupies 256 bits, which are written as 64 hexadecimal characters. NIST includes it in the federal standard. FIPS 180-4Unlike encryption, a hash cannot be undone with any key. Bitcoin uses it to link blocks and measure mining effort.
Understanding how it works helps you distinguish what this function truly protects and what depends on other parts of it. Bitcoinsuch as node consensus and network computing power. It also allows you to detect exaggerated claims, for example, that a quick hash is sufficient for storing passwords, something the OWASP guide itself advises against. Clarifying these limits is the quickest way to avoid confusing a mathematical function with a complete security system.
 Certificate
What is the SHA-256 algorithm?
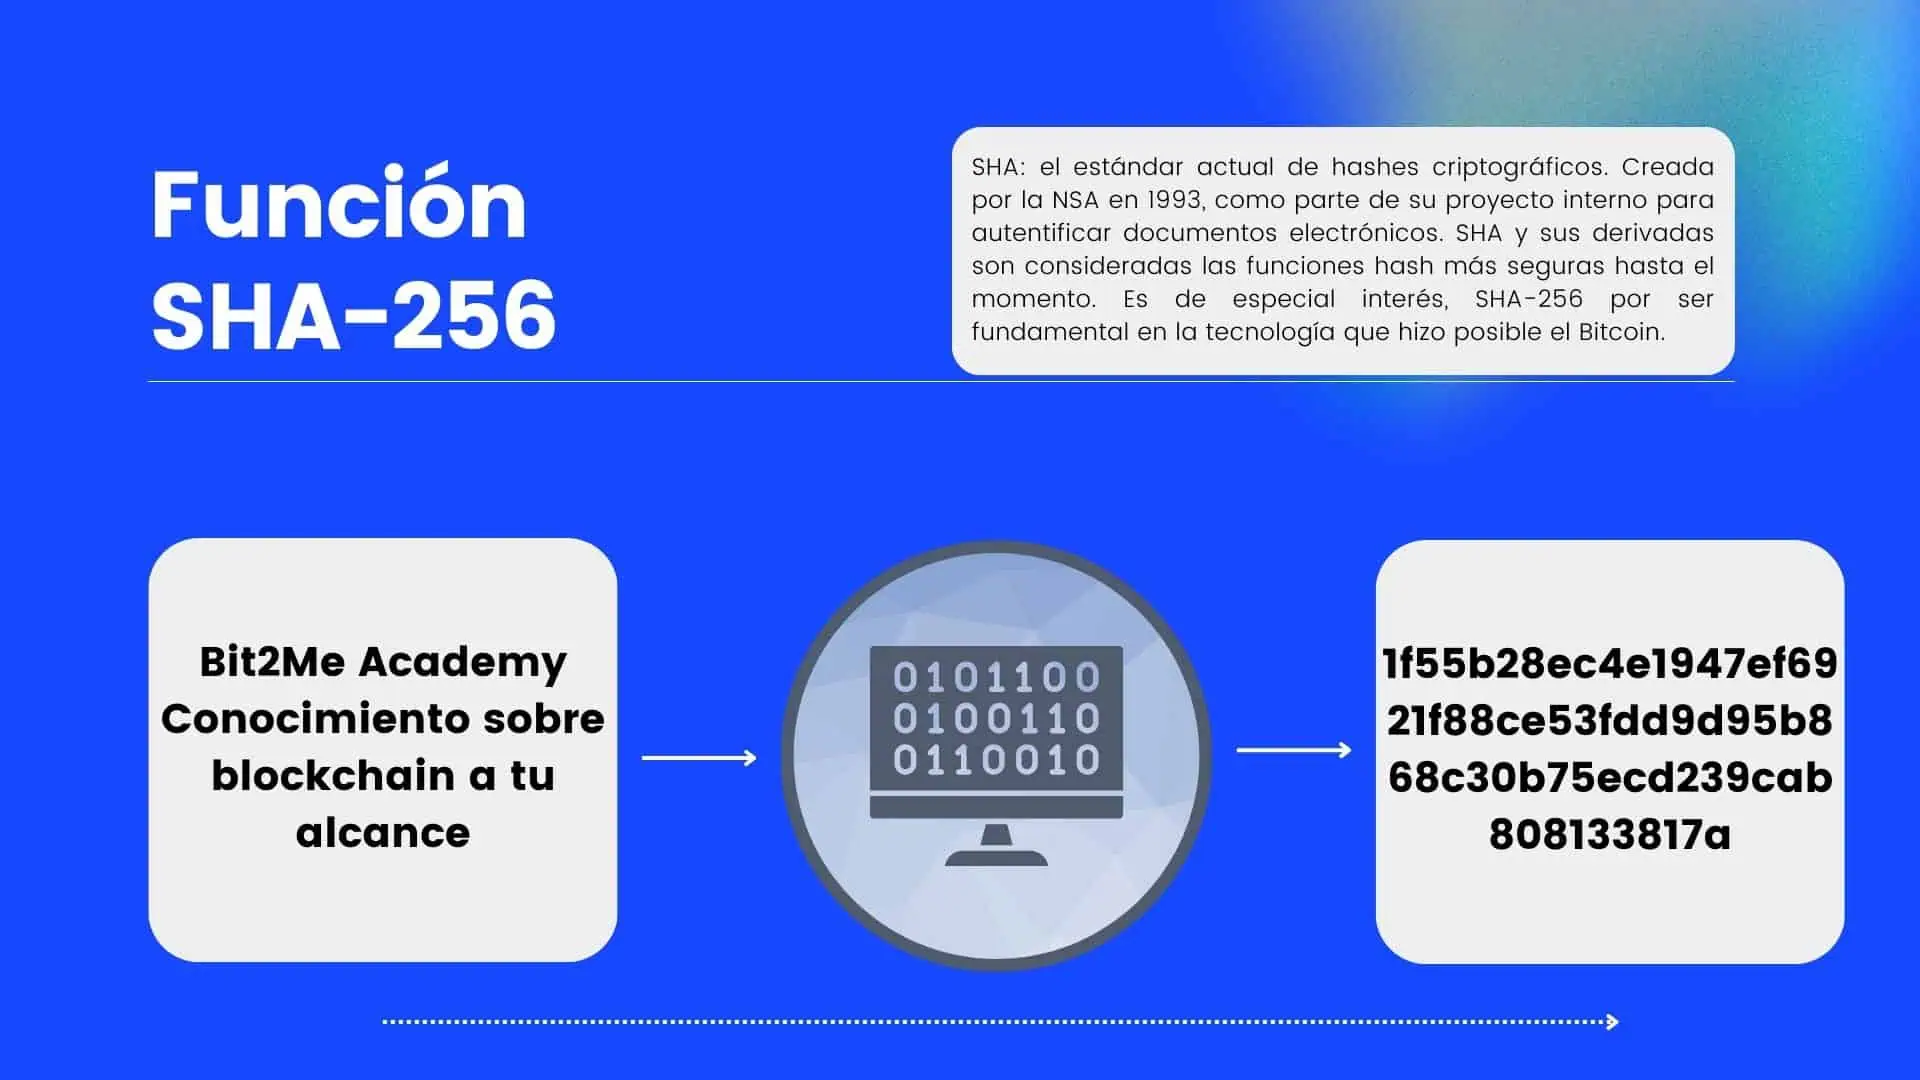
SHA-256 stands for Secure Hash Algorithm 256-bit, one of the functions in the SHA-2 family specified by NIST in FIPS 180-4. A hash function takes an input of any size—be it a phrase, a file, or a block header—and summarizes it into a fixed-length string that acts as a digital fingerprint of the original content. If you want to review the general concept, how a hash function works He explains it from scratch.
The function is deterministic, meaning the same input always produces the same output, and it's unidirectional: calculating the hash of a piece of data is immediate, but retrieving the data from the hash is only possible by testing inputs one by one. Furthermore, the output is always 256 bits, whether you input a single letter or a file of several gigabytes.
There are infinitely many possible inputs and only 2 to the power of 256 outputs, so in theory two different inputs can produce the same hash, a phenomenon called a collision. In practice, finding one intentionally would require on the order of 2 to the power of 128 operations using the birthday attack, a number beyond the reach of current computing.
What is a SHA algorithm?
The first version of the family, known as SHA-0, was published in May 1993 as NIST's FIPS 180 federal standard, which retired it in April 1995, replacing it with SHA-1. This second version remained in use until practical collision attacks emerged, and NIST declared it obsolete in 2011.
The current NIST timeline sets December 31, 2030, as the date after which FIPS 140 validated modules that still support SHA-1 will be relegated to the historical list. By then, the recommendation is to use SHA-2 or SHA-3 in all applications.
SHA-2 is a family of six functions, including SHA-256 and SHA-512, all of which are listed in FIPS 180-4. SHA-3, defined in the FIPS 202 standard, uses a different Keccak-based construct and was not created to replace SHA-2, because NIST itself states that there is no need to migrate from one to the other.
How does SHA-256 work?
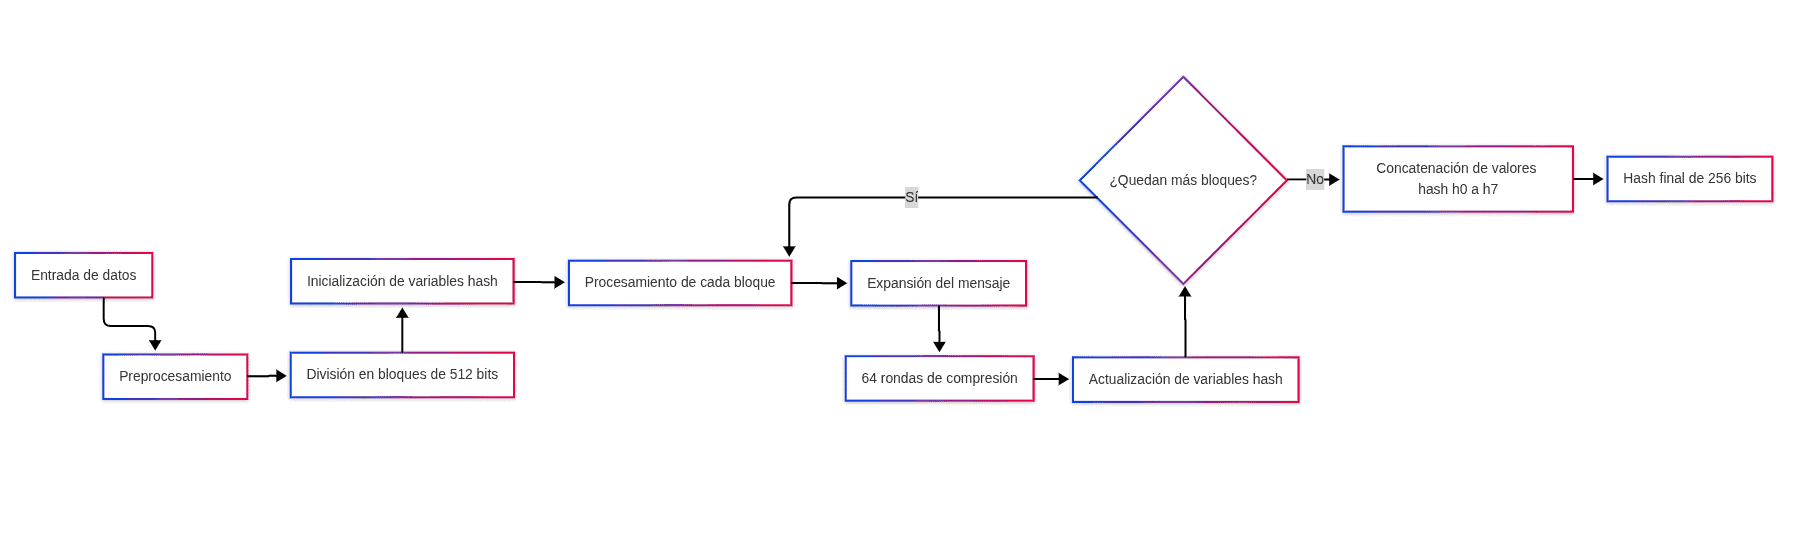
SHA-256 processes the message in 512-bit blocks and repeats the same steps with each one until a 256-bit digest is obtained. Although the internal operations are bit additions and shifts, the overall scheme is easily understood in five stages that follow the FIPS 180-4 standard.
- Preprocessing: the message is completed with padding and its length to form 512-bit blocks.
- Initialization: the algorithm starts from eight 32-bit values, from h0 to h7, which is set by the standard.
- Expansion: each block expands to a 64-word, 32-bit address book.
- Compression: 64 rounds mix those words with standard constants using bitwise addition and operations.
- Result: After the last block, the eight values h0 to h7 are concatenated and form the 256 bits of the hash.
This design explains why the input size doesn't change the output size, and why any alteration to the message propagates through all rounds. To go further, the PDF Cryptography: SHA-256 FunctionThe algorithm, by Javier Domínguez Gómez and hosted on Academy, develops the algorithm in more technical detail.
What is the avalanche effect?
A well-designed hash function responds to even the smallest change with a result that bears no resemblance to the original: altering just one letter of the input can almost completely change the output. Because of this property, the input cannot be deduced by comparing similar hashes, since similar hashes do not exist to reveal similar inputs.
The table below shows it with two entries that differ only by a capital letter. The hashes were calculated using Python's hashlib library on October 30, 2026, encoding the text in UTF-8 and without a trailing line break.
| Entry | Hash SHA-256 |
|---|---|
| Bit2Me Academy | b35937a6ee578fa550000f9fd122f89182b5f4697fccefdbf26c8778c4880da4 |
| Bit2Me academy | b0beaada4e84b9089a0de57a369988aa6ca08de4226ff602bdd86e3f9e57f7fd |
Of the 256 bits in each result, 145 are different between the two inputs, slightly more than half. This proportion is expected in a good hash function, because each output bit should behave as if it depended equally on all the input bits.
You can repeat the test on your computer with printf 'Bit2Me Academy' | sha256sum and then with a lowercase "a", and you'll get the same hashes as in the table. Use printf and not echo to avoid adding a line break, because that extra character would also change the result.
For Bitcoin, this property is the foundation of miners' work. Since there's no shortcut to approaching a specific hash, the only strategy is to try different inputs and check the result, and the network can adjust how much effort that search requires.
How does Bitcoin use double SHA-256 in each block?
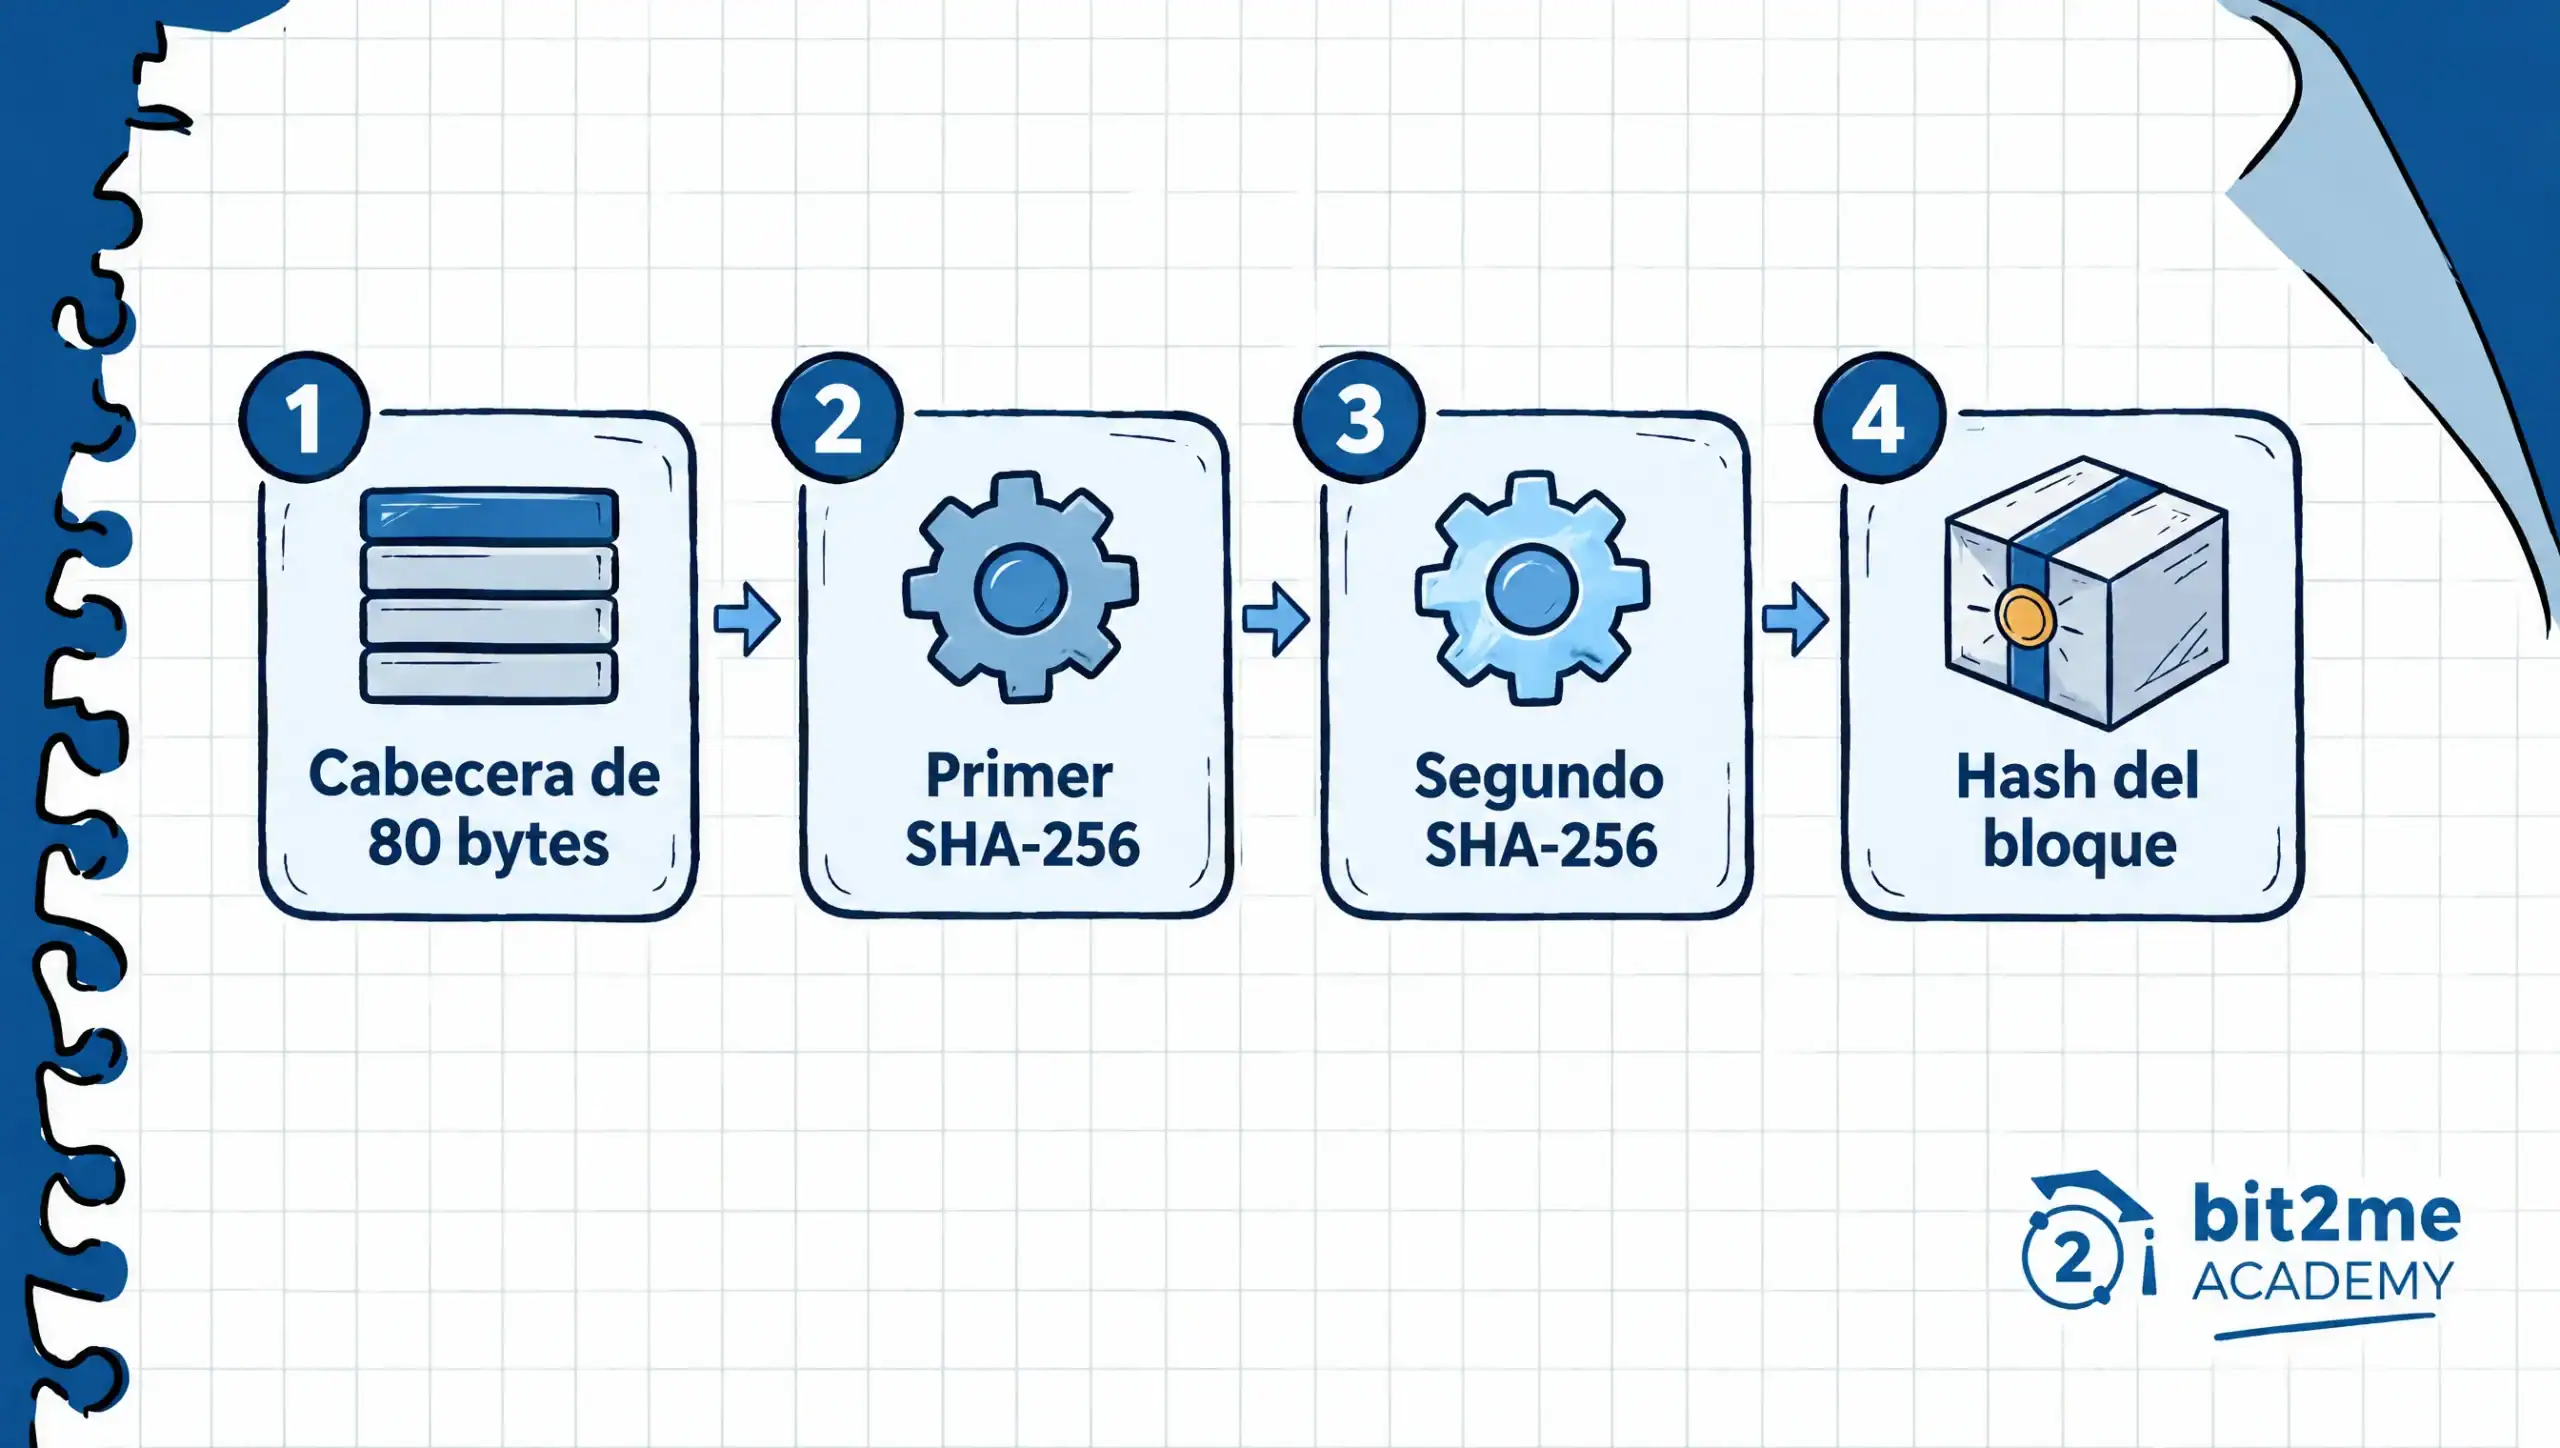
Two consecutive passes of the same function, written SHA256(SHA256()), produce the hash of the header of each block and those of each pair in the Merkle tree, according to the Bitcoin developer documentationThe result of the first pass is the input for the second.
Each block summarizes its transactions in a Merkle tree. Transaction identifiers are taken in pairs, concatenated, and double SHA-256 is applied to form the next row, and so on until a single hash remains, the root of the Merkle tree. If a row has an odd number of hashes, the last one is duplicated.
That root travels within the block header, which is 80 bytes long. Inside are the hash of the previous block and the Merkle root, along with the timestamp, difficulty target, and nonce. The hash in that header identifies the block, and only those 80 bytes are processed for proof of work.
This is where the immutability of the chain comes from. If someone were to modify an old transaction, they would change the Merkle root, then the header, and then the hash that stores the next block, so that all subsequent blocks would no longer fit together.
When a node receives a block, it recalculates the double SHA-256 hash of the header and checks that it doesn't exceed the current difficulty target; if anything seems off, it discards the block. You can see how to assemble one in the guide for set up a Bitcoin node, and how each transaction is structured Complete the table.
How does SHA-256 relate to mining difficulty?
Mining involves changing the header nonce and recalculating its SHA-256 double hash until a hash is found that does not exceed a maximum value, the network's objective, as explained in the block guide. developer.bitcoin.orgThe lower the target, the fewer hashes meet it and the more attempts are needed on average. Each additional bit of zeros at the beginning of the required hash halves the number of valid hashes and therefore doubles the average number of attempts.
The network recalculates the difficulty every 2.016 blocks, measuring how long the last blocks took to complete using the timestamps. The difficulty increases when blocks were completed too quickly and decreases when they took too long. With an ideal timeframe of two weeks for those 2.016 blocks, the target pace is one block every ten minutes.
This connection explains why the hashrate, the number of hashes the network calculates per second, is measured today in exahashes. One EH/s is equivalent to one trillion, or 10 to the power of 18 hashes per second, so the 900 EH/s in August 2026 is about 9 times 10 to the power of 20 SHA-256 calculations every second. If you want to see the practical side, What is cryptocurrency mining? Describe the process from the miner's perspective, and you can consult the Bitcoin price today en Bit2Me.
Features of the SHA-256 algorithm
SHA-256 has four properties that explain its widespread use: it is deterministic, always producing a 256-bit hash; it is unidirectional; and it is collision-resistant with current computing power. Furthermore, it is efficient, balancing security and computational cost, and can be implemented on anything from a server to a modest machine without sacrificing processing speed.
The following table places SHA-256 alongside other functions with the same history. Size and status data are from NIST (FIPS 180-4, FIPS 202 and its policy on hash functions), accessed on October 30, 2026.
| Algorithm | Family | Hash size | Situation according to NIST |
|---|---|---|---|
| SHA-1 | SHA-1 | 160 bits | Discouraged since 2011; validated modules lose it after 31-12-2030 |
| SHA-256 | SHA-2 | 256 bits | Approved under FIPS 180-4 |
| SHA-512 | SHA-2 | 512 bits | Approved under FIPS 180-4 |
| SHA3-256 | SHA-3 | 256 bits | Approved in FIPS 202 |
The standards distinguish three types of resistance. Preimage resistance requires that, given a hash, no input can be found that produces it. Second preimage resistance prevents finding another input with the same hash as a known one, and collision resistance prevents finding any pair of matching inputs.
The difference between SHA-256 and SHA-512 goes beyond the output size. SHA-512 works with 1.024-bit blocks and 64-bit words, while SHA-256 uses 512-bit blocks and 32-bit words. This is why Bitcoin uses SHA-256, and the choice between the two depends on the system, not on one being more secure overall.
SHA-256 applications beyond Bitcoin
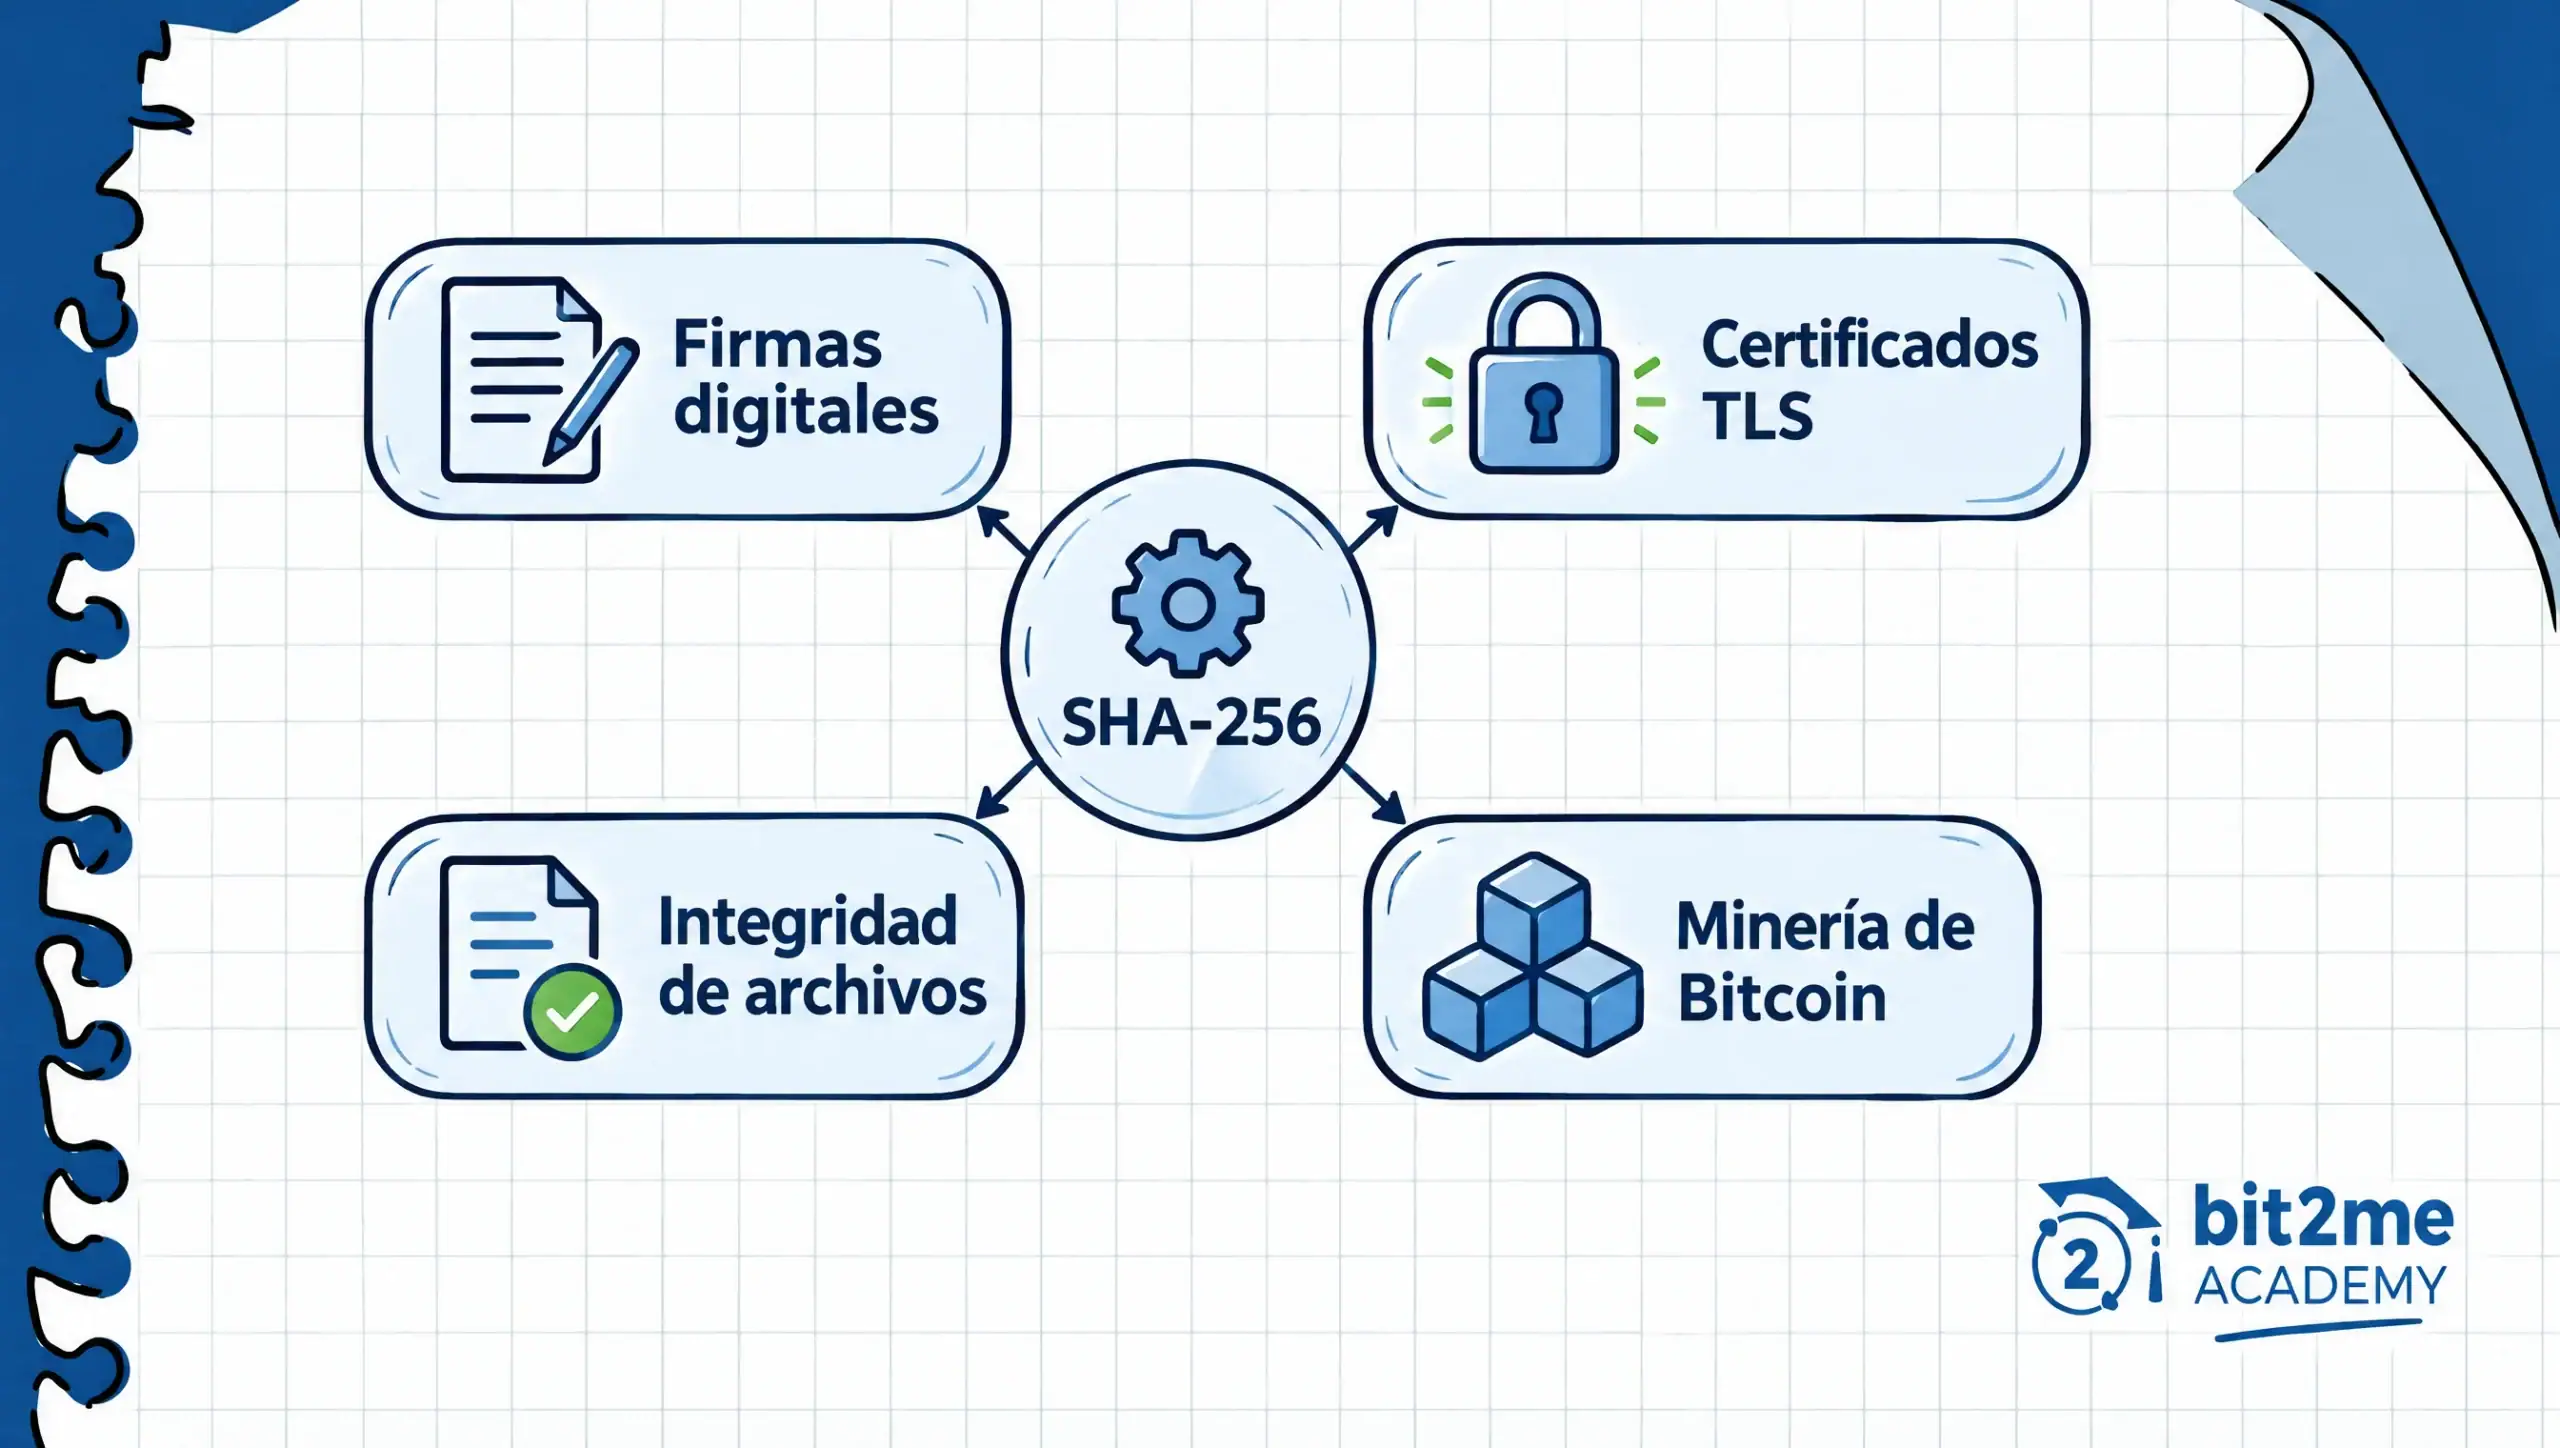
SHA-256 appears in many systems that have nothing to do with cryptocurrencies. Digital certificates and electronic signatures are calculated based on the hash of the content, so any subsequent changes invalidate the signature. In a TLS connection, SHA-256 verifies integrity and backs up signatures, but the encryption of the traffic is handled by other algorithms.
The most common application is download verification. Many projects publish their SHA-256 hash alongside a program, and you can calculate the hash of the downloaded file with... sha256sum archivo on Linux, shasum -a 256 archivo on macOS or Get-FileHash archivo in PowerShell. If both hashes match, the file is the one published by the developer, without corruption or manipulation along the way.
Git is another case where clarification is necessary. By default, Git identifies each commit with SHA-1, and offers SHA-256 as an optional repository format. Its documentation on incompatible changes (Breaking Changes) anticipates that SHA-256 will become the default hash in Git 3.0, with no confirmed date until October 2026.
With passwords, the common mistake is thinking that simply applying SHA-256 is enough. OWASP guide It states that fast algorithms like SHA-256 are unsuitable for password storage because they allow for testing an enormous number of combinations per second. It recommends Argon2id first and scrypt as an alternative, leaving bcrypt for legacy systems and reserving PBKDF2 with HMAC-SHA-256 and 600.000 iterations for those who need to comply with FIPS-140.
Current status of SHA-256
The security of SHA-256 is evaluated against the official source, and direct verification at csrc.nist.gov is more reliable than any article, including this one. The table reflects the status of the most frequently changing data as of October 30, 2026.
| Date | Situation | Source and date |
|---|---|---|
| FIPS 180-4 | Effective since August 2015; review announced in March 2023 and without FIPS 180-5 published | NIST, 30-10-2026 |
| SHA-2 vs. SHA-3 | Without needing to migrate from one to another | NIST, policy on hash functions |
| SHA-1 | Validated modules will lose their validity after 31-12-2030 | NIST, December 2022 |
| Go | SHA-1 by default; SHA-256 by default as provided in Git 3.0, no date | Git, BreakingChanges, 10-30-2026 |
| Bitcoin Hashrate | About 900 EH/s, compared to a previous high of 1,14 ZH/s | 18-08-2026 |
Hashrate is the fastest-changing metric, so it's best to consult recent data before citing it. The drop to 900 EH/s recorded in August 2026 occurred because less profitable miners shut down their equipment, not because the hash function itself changed.
The next Bitcoin halving is scheduled for 2028. This event halves the block reward, but does not change the network's hash function, which remains the double SHA-256 until the developers decide otherwise.
Why SHA-256 remains the foundation of Bitcoin
After examining the SHA-256 algorithm from the inside, it becomes clear that it's not the only thing that sustains the network. This function provides the digital fingerprint of each block and demonstrates the work required to add it, but Bitcoin's security also depends on consensus among thousands of nodes and the total computing power that miners contribute.
This combination explains why the function has been in use for over fifteen years without a practical way to break it, and why any future change would require broad agreement from the entire community. If you want to know what asset SHA-256 protects, you can buy Bitcoin at Bit2Me and see for yourself how each transaction is recorded in a block.

Frequently Asked Questions about SHA-256


 Author