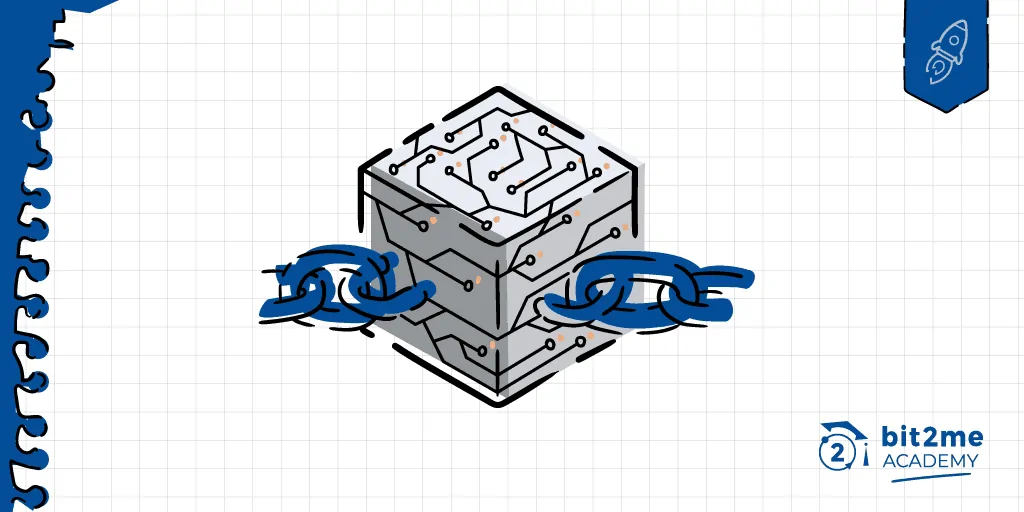
Essential Points
- Immutable Storage Unit: A block acts as a digital container that records validated transactions, ensuring that the data cannot be modified once confirmed by the network.
- Security through Hashing: Integrity is maintained through the chaining of hashes; each block is a piece of a cryptographic puzzle that depends directly on the previous piece.
- Critical Technical Components: It essentially consists of a "Header" (metadata such as the Nonce and Timestamp) and a "Body" (the list of transactions), allowing for a transparent and public audit.
- Consensus Mechanism: The creation of new blocks is not arbitrary, but requires the resolution of mathematical challenges or the validation of shares, depending on the protocol (PoW or PoS).
Imagining a global network processing thousands of financial transactions every minute without a consolidation structure would be like visualizing absolute technical chaos. For the registration of a digital asset to be viable, we cannot validate each transaction in isolation; the system would collapse from sheer resource exhaustion. This is where the concept of a blockchain comes into play, an engineered solution designed to package information and ensure that everything fits together seamlessly within the blockchain.
The heart of validation
To understand why Proof of Work (PoW) is the cornerstone of security in this ecosystem, we must stop viewing mining as a simple process of "manufacturing" coins and start seeing it as a safeguarding mechanism. It's not just about creating new crypto assets, but about making lying to the network so costly that no one dares to try.
The Enigma: SHA-256 and Adjustable Difficulty
When we say that computers solve a "puzzle", we mean finding a specific hash that meets a condition imposed by the protocol: it must start with a certain number of zeros.
This process is purely trial and error. Miners modify a small data field called a nonce and run the entire block through the hashing algorithm repeatedly. It's like trying to find the combination to a million-digit safe by trying each digit one by one.
- Automatic adjustment: If there are more miners (more power), the network increases the difficulty by requiring more zeros at the beginning of the hash.
- The objective: Maintain a stable transmission time of around 10 minutes. If blocks were generated in seconds, the network wouldn't have time to synchronize and total chaos would ensue.
The Hash as a Seal of Integrity
What happens if an attacker wants to modify a transaction from three blocks ago? This is where the structure becomes brilliant. Each block includes the hash of the previous block.
If you change a single bit in Block 1:
- Its hash changes completely.
- Since Block 2 stored the original hash of Block 1, the connection is now broken.
- For Block 2 to become valid again, the attacker would have to mine it again (spending a huge amount of energy).
- But when Block 2 is changed, the hash of Block 3 is also broken… and so on.
To rewrite history, you would need to control more than 51% of the world's computing power. Currently, the electricity and hardware costs to achieve this are so astronomical that it's more profitable to be an honest miner and receive rewards than to attempt to attack the system.
Efficiency through aggregation
Validating transactions one by one would be like trying to seal each grain of rice in a sack separately. By putting them into a block and generating a Merkle Root, we seal the entire "sack."
This structure allows any node in the network to verify the validity of thousands of transactions with a single mathematical calculation. Your computer doesn't need to check each signature individually every time it connects; it simply needs to verify that the block's hash is correct and fits perfectly into the chain coming from the source.
Is it really worth spending so much energy to secure a ledger? If what we're looking for is a network resistant to state censorship and global-scale attacks, the technical answer is a resounding yes. Without that energy expenditure, the digital asset would lose its most valuable property: immutability.

Anatomy of an Information Node
The internal structure of a block is not random. Its header contains traces of the previous block, creating the unbreakable link we call a chain. This is further reinforced by timestamps, the nonce—the random number miners look for—and the key component: the Merkle Tree.
This substructure functions as a hierarchical digest. Instead of storing each individual piece of data, a root, or Merkle Root, is generated that summarizes all the transactions in the block. If someone were to try to change even a single cent of a past transaction, the root would change, and the block would be instantly invalidated. It's mathematics applied to trust.
Inside the Block: Much more than data
If we dissect a block, the first thing we find is a clear division between the header and the body. The body is simply the listing of transactions, but the header is where the magic happens that allows your computer to trust the network without knowing anyone.
The header components
- Hash of the previous block: It's the glue of the chain. By including the digital fingerprint of the previous block, any alteration in the past would require changing all subsequent blocks. This is what makes the technology, in practice, immutable.
- Timestamp: It indicates the exact time the block was mined. This prevents anyone from trying to "rewrite" the chronological order of events.
- Nonce: It's the variable that miners frantically modify. Since all other data is fixed, the nonce is the only piece they can touch to try to make the resulting hash meet the difficulty required by the network.
Merkle Root: The Big Summary
How can we be sure that among thousands of transactions, no one has changed a single comma? This is where the Merkle Tree comes in. Instead of checking the entire list over and over, the system uses a binary tree structure where transactions are paired and combined into new hashes until they are reduced to a single code: the Merkle Root.
Imagine you have a block with 2.000 transactions. If you change a single character in transaction number 1.500, the hash of that branch changes. That change propagates upwards like a domino effect until the Merkle Root is completely different.
Why is this a technical marvel?
- Ultra-fast verification: A node doesn't need to download the gigabytes that make up the entire history of the cryptocurrency to know if a transaction is valid. It only needs the hash path (Merkle Path) that connects that transaction to the root.
- Space saving: It allows for the existence of "lightweight nodes" on devices with limited memory, such as your mobile phone. You can verify your payments without being a massive data server.
- Mathematical certainty: If the root matches, the information is complete. There is no middle ground or possible interpretations.
Do we really need this level of sophistication to move value over the internet? If we want to avoid double-spending without relying on a central bank for permission, the answer is that this tree is the only real barrier against fraud.
Pages from an Infinite Book
It's often said that a blockchain is a ledger. If we accept that premise, each block represents one of its pages. Once a page is filled and validated, it's "passed" and can no longer be deleted or removed from the ledger. Everything that happens on the network is recorded there forever, visible to anyone who wants to verify it.
However, not all web pages are the same, nor are they written at the same speed. Each network sets its own rules, limiting block size and the time that must pass between blocks to avoid saturation.
Immutability: Pages that turn to stone
When we say a page "passes," we mean the exact moment the network consensus validates a block. From that point on, the information becomes immutable. It's not that deleting data is technically impossible; it's that the cost of doing so is so prohibitive that no one in their right mind would attempt it.
Total visibility: Any of you, from your computer or mobile device, can consult any page written since the beginning of time. It's absolute transparency: there's no need to trust what an entity says, simply verify the record.
The sealing: Each new page contains a summary of the previous one. If you were to try to tear out page 50, all pages from 51 onward would be immediately invalidated. The book would "realize" the sabotage.
The Writing Dilemma: Speed vs. Space
This is where theory clashes with technical reality. If a ledger has infinite pages but only one can be written every ten minutes, what happens if millions of people want to record their transactions at the same time? A queue forms, known as a mempool.
Each cryptocurrency network has made a different design decision to manage this flow:
- Page size (Block Size): If we create very large pages, we can fit more transactions, but the ledger becomes so heavy that only a few people could load it. This would jeopardize decentralization, since only large companies would have servers capable of handling such a volume.
- The writing frequency (Block Time)If we write a page every few seconds, the system is faster, but it increases the risk of synchronization errors or "orphan pages" that fail to join the main book.
Own Rules of the Game
Currently, the debate is not whether the book works, but how to optimize it. While some networks prefer to keep pages small and secure, delegating speed to "secondary layers," others have opted to expand their limits to try to process everything on the main chain.
Do we really need every coffee purchase in the world recorded in the main ledger? Probably not. Modern efficiency hinges on understanding that not all data has the same value or requires the same level of security.
FAQ – What is a block in blockchain?


 Author